Case Study: Conference Arcade Machine
At Cyberus Technology, we developed a custom arcade machine to showcase our expertise at conferences and trade shows. This system runs a simple game on Cyberus Linux and serves as an excellent demonstration of Cyberus Linux benefits in practice.
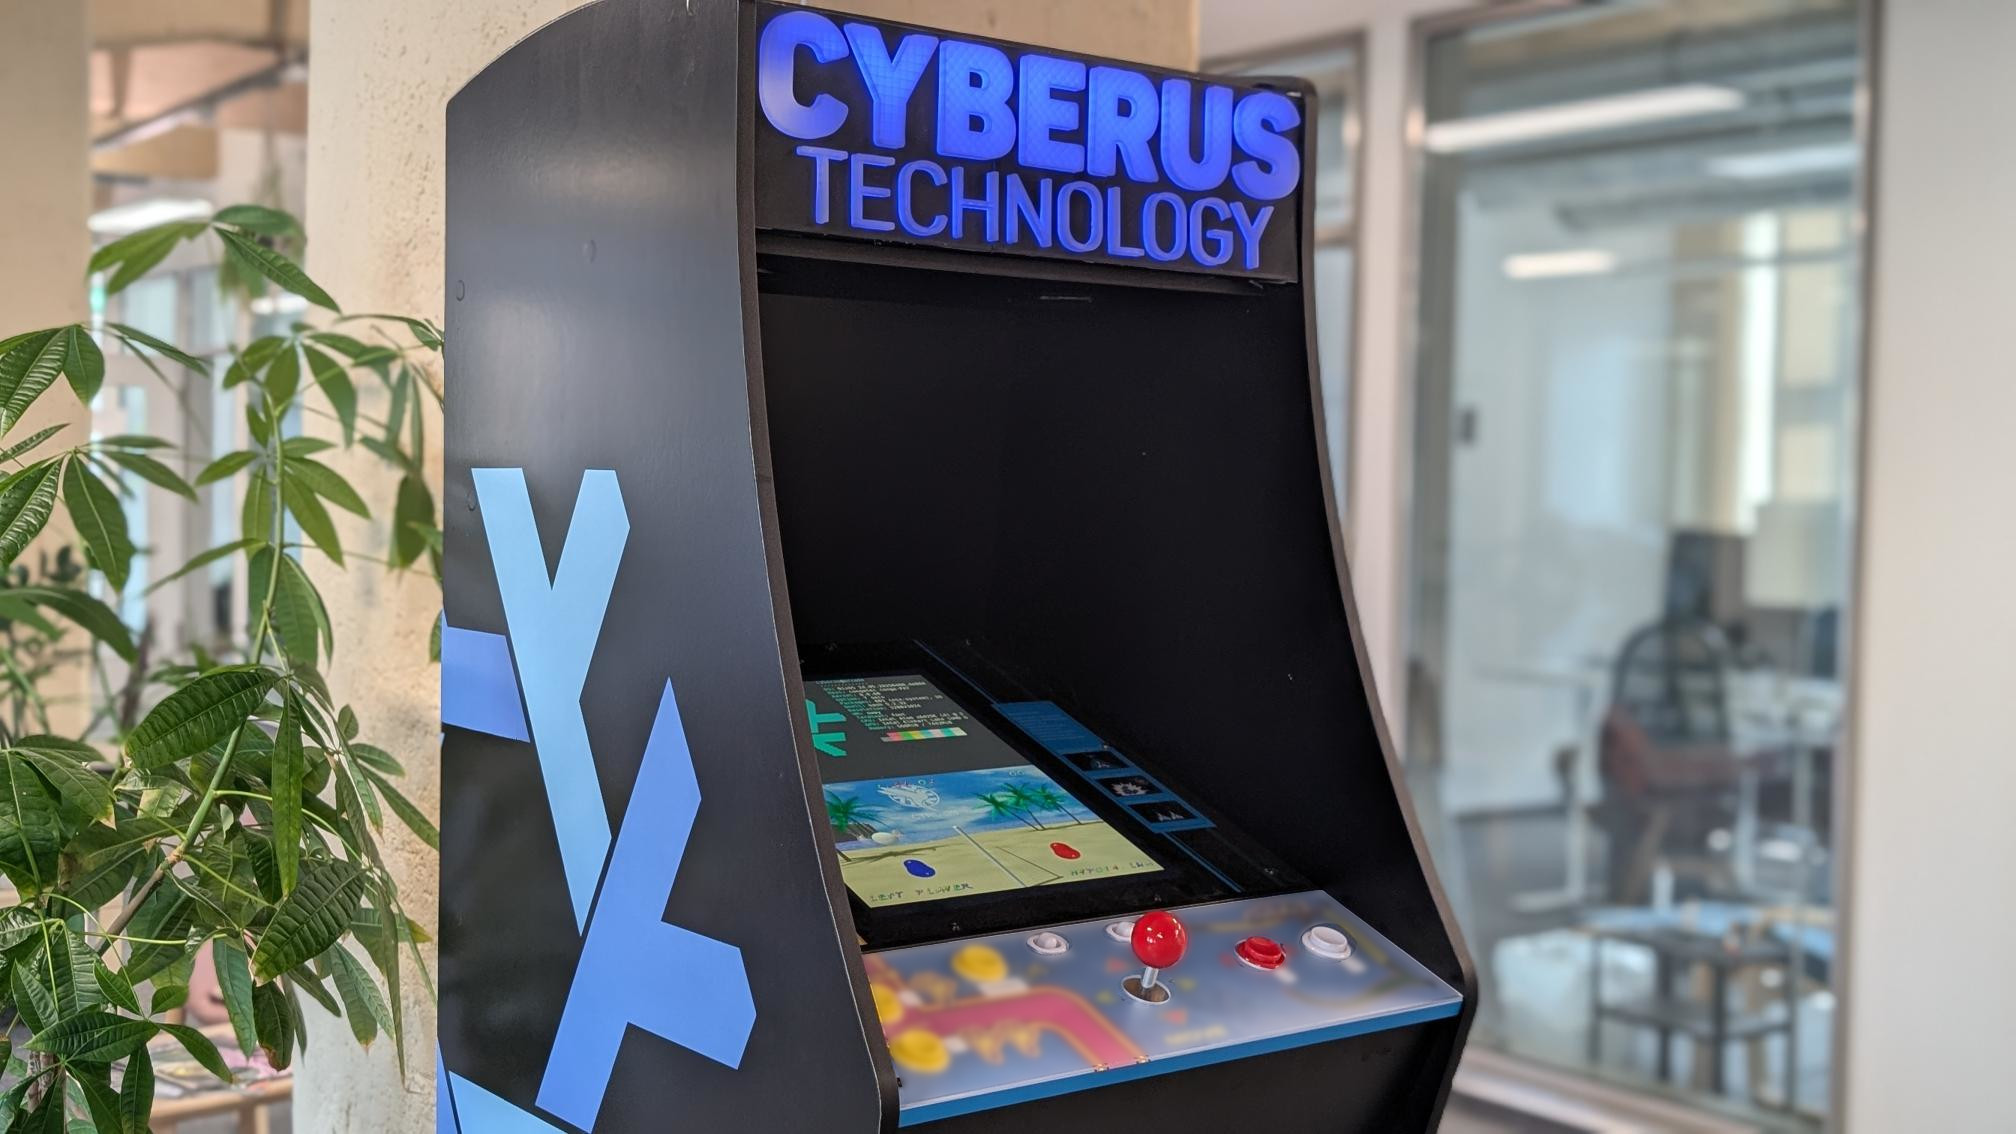
Creating a Secure & Maintainable Conference Demonstrator with NixOS
Our arcade machine travels to conferences throughout the year, requiring security updates before each event. However, the scheduled EOL date for NixOS 26.05 is at the end of December, which is far before the expected EOL for our arcade machine. For CRA compliance this is a non-starter.
Cyberus Linux 26.05 provides:
- Continued security updates for unmaintained NixOS versions
- Minimal maintenance overhead
- Consistent, reliable deployments
From NixOS to Cyberus Linux
The arcade machine runs on x86 hardware with Sway as the window manager and a game that starts automatically at boot. The original configuration uses standard NixOS packages:
{
  description = "NixOS configuration of the arcade machine";

  inputs.nixpkgs.url = "github:NixOS/nixpkgs/nixos-26.05";

  outputs = { nixpkgs, ... }: {
    nixosConfigurations = {
      "arcade" = nixpkgs.lib.nixosSystem {
        modules = [
          ./nixos/configuration.nix
          ./nixos/hardware-configuration.nix
        ];
      };
    };
  };
}
Migrating to Cyberus Linux requires a single line change: Update the Nixpkgs input to use the Cyberus Linux release channel:
{
  description = "NixOS configuration of the arcade machine";

  inputs.nixpkgs.url = "https://channels.cyberus-linux.com/channel/cyberus-linux-26.05.tar.xz";

  outputs = { nixpkgs, ... }: {
    nixosConfigurations = {
      "arcade" = nixpkgs.lib.nixosSystem {
        modules = [
          ./nixos/configuration.nix
          ./nixos/hardware-configuration.nix
        ];
      };
    };
  };
}
The migration is complete! With this single change, the arcade machine now receives security updates through Cyberus Linux 26.05 until 2031.
Generating SBOMs
Follow our SBOM generation guide to learn how to continuously generate up-to-date SBOMs as part of your CI.
Cyber Resilience Act Compliance & Security Improvements
Without Cyberus Linux, we have three options:
- Become vulnerable to any CVE discovered after December 2025. This is not an option for the European market because the Cyber Resilience Act (CRA) requires fixing any vulnerabilities in products on the market.
- Update all packages ourselves. This may be feasible for smaller projects, but requires multiple engineering days a months to classify CVEs, implement, and test updates.
- Upgrade to a newer NixOS release. Again, this requires engineering effort to implement and test the upgrade. Certified use-cases often require an additional re-certification.
Cyberus Linux provides immediate security benefits and insight into the state of discovered vulnerabilities via its Security Tracker.
Enabling Long-Term Secure NixOS Systems with Cyberus Linux
Migration Benefits
- Single-line configuration change (Nixpkgs input URL)
- Zero downtime during migration
- All existing functionality & certifications preserved
- Continued security maintenance for unmaintained NixOS versions
While upgrading to a newer NixOS version would also provide security updates, this approach is often impractical for certified systems that require expensive re-certification after major version changes. Cyberus Linux solves this problem by providing security updates within the same NixOS version, eliminating certification concerns.
This case study demonstrates how Cyberus Linux enables organizations to maintain secure, up-to-date NixOS systems with minimal operational overhead - particularly valuable for certified systems where version upgrades are cost-prohibitive.